Хиймэл оюун ухаанд суурилсан тус компани байгууллагын аюулгүй байдал болон дагаж мөрдөх журмын үйл ажиллагааг автоматжуулах шийдлээ өргөжүүлэхээр төлөвлөж байна
Кибер аюулгүй байдал болон дагаж мөрдөх журмын хэрэгжилтийг хариуцдаг Comp AI стартап пүрэв гарагт 34 сая долларын А шатны санхүүжилт татсанаа зарлав. Roo Capital болон Grand Ventures компаниудын тэргүүлсэн энэхүү хөрөнгө оруулалтаар тус компанийн нийт босгосон хөрөнгийн хэмжээ 37.5 сая долларт хүрч байна.
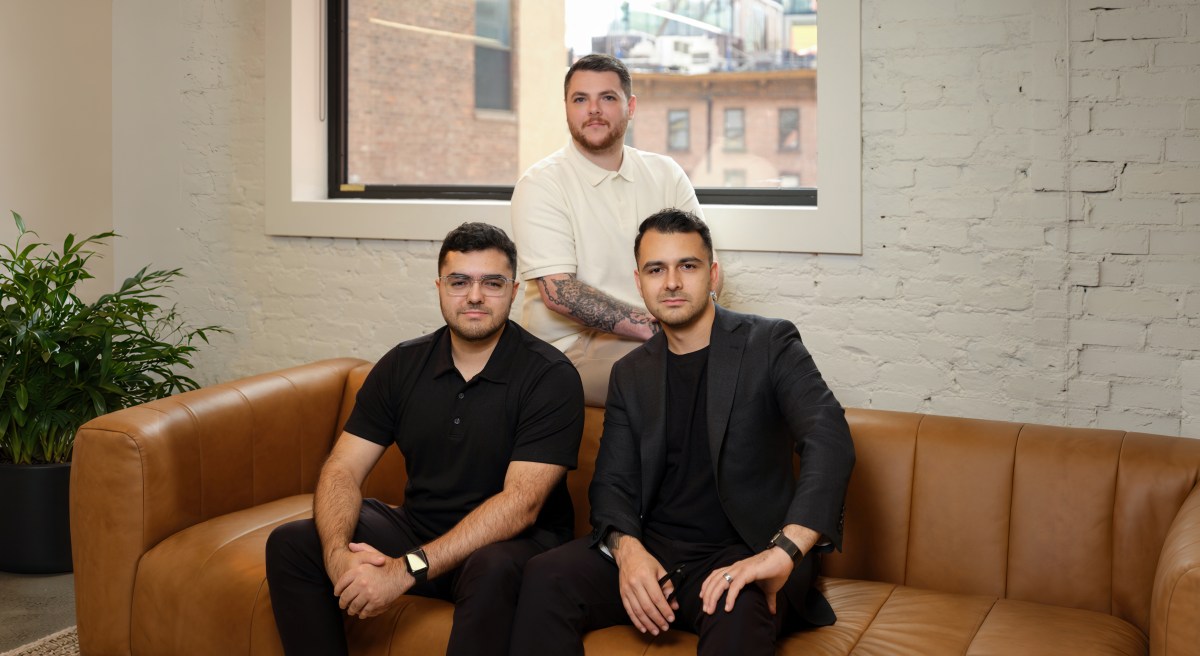
Comp AI компанийг Льюис Кархарт, Клаудио Фуэнтес, Мариано Фуэнтес нар өнгөрсөн нэгдүгээр сард үүсгэн байгуулжээ. Үүсгэн байгуулагчид нь өмнө нь LeapAI платформыг хөгжүүлж байсан туршлагатай бөгөөд тухайн үед SOC 2 дагаж мөрдөх журмын үйл явц нь маш төвөгтэй, цаг хугацаа их шаарддаг болохыг олж мэдсэн нь энэхүү стартапыг эхлүүлэх гол сэдэл болсон байна.
Тус платформын гол зорилго нь хиймэл оюун ухааны агентуудыг ашиглан компанийн аюулгүй байдлын бодлогыг боловсруулах, аудитын нотлох баримт цуглуулах, хяналтын журмын хэрэгжилтийг тасралтгүй хянах зэрэг ажлыг автоматжуулахад оршино. Мөн уг систем нь дэд бүтэц болон кодын санд гарч болзошгүй эмзэг байдлыг илрүүлэх хиймэл оюун ухаанд суурилсан нэвтрэлтийн туршилтыг (penetration testing) гүйцэтгэдэг.
Хэдийгээр тус платформ нь аюулгүй байдлын шаардлагуудыг хангах үйл явцыг автоматжуулдаг ч хүний оролцоог бүрэн орлохгүй гэдгийг үүсгэн байгуулагчид онцоллоо. Хиймэл оюун ухааны бэлтгэсэн бодлого болон бусад чухал шийдвэрүүдийг хүн хянаж, баталгаажуулах зарчмаар ажилладаг бөгөөд технологи хөгжихийн хэрээр хяналтын тогтолцоог улам бэхжүүлэх нь чухал юм.
Дэлгэрэнгүйг эх сурвалжаас харах
↓Эх сурвалжийг нээх ↓
Comp AI, a cybersecurity and compliance startup, announced that it has raised a $34 million Series A round on Thursday. The round was led by Roo Capital and Grand Ventures.
The company was founded last January by Lewis Carhart (CEO), Claudio Fuentes (COO), and his brother, Mariano Fuentes (CTO). Claudio and Mariano had been building startups together for nearly a decade, met Carhart a few years ago, and invited him to join LeapAI, a workflow platform they were building. Claudio was the CEO and co-founder, while Carhart served as head of growth and Mariano was a senior full-stack engineer. The startup ran for about two years, growing to more than a million users, but they eventually decided to shut it down after not finding a “sticky enough use case to warrant continued investment.”
That experience taught them a lot, though, they recalled. For one, they learned how to build with LLMs and the importance of finding a specific use case for a product. They also learned how tedious the SOC 2 compliance process was, especially as they tried to scale the platform to work with bigger enterprise clients.
“It’s a very obscure process,” Claudio said. “It took us a couple of months of doing things by hand, and the whole time it meant taking our eyes off building the product.”
Alas, a startup idea was born. This time, Carhart would take the lead as CEO because it was his idea, the trio said. Comp AI says it’s building an agentic platform to tackle tedious security and compliance work; that means having AI agents help write company security policies or collect evidence for security audits. The platform also continuously monitors whether a company is meeting compliance controls. Comp AI is part of the next generation of cybersecurity startups emerging to help companies run more efficiently in the agentic era.
“For a lot of software companies, security and compliance are directly tied to revenue,” Carhart told TechCrunch, citing, for example, how a customer might ask a startup for a SOC 2 report before closing a deal. “What Comp AI automates is much of the work companies traditionally have to do around that process.”
The software helps companies meet and maintain those security requirements, he continued, but doesn’t replace actual independent audit review. It also doesn’t replace humans, the trio said. Human workers help onboard the AI, support controls, and maintain the agentic workflow.
“An agent might draft a policy, for example, but a person still reviews and approves it,” Carhart said. “As agents take on more consequential actions over time, we believe the level of safeguards and human approval should increase accordingly.”
The company also offers AI-powered penetration testing, “where the platform proactively tests codebases and infrastructures for vulnerabilities,” Carhart said. The team hopes this Series A capital will help with product expansion. It has raised $37.5 million in funding to date.
There has been much conversation about the new wave of security risks in the agentic era (and with it, a wave of AI security and compliance companies like Vanta and Drata). Carhart said the rapid adoption and experimentation companies are doing with AI is creating a need for continuous — and perhaps autonomous — security and compliance platforms.
“Imagine a company completes its SOC 2 audit and two weeks later deploys a new AI agent that can access customer data, change permissions across an internal system, or introduce a new vulnerability through code deployment,” he said. “The audit didn’t become invalid; it simply wasn’t designed to tell you in real time what changed afterward.”
As companies adopt more AI, Mariano said, they also need to show what an agent accessed, what it tried to do, and whether it stayed within the boundaries given. Comp AI is tackling this by starting with permissions and accountability, he continued. “We’re building toward a security layer that can monitor and validate those kinds of risk more continuously as these systems evolve.”
When you purchase through links in our articles, we may earn a small commission. This doesn’t affect our editorial independence.