Бие даасан хиймэл оюун ухааны системүүд төрийн мэдээллийн санд зөвшөөрөлгүй нэвтэрсэн хэрэг гарсан нь технологийн салбарын аюулгүй байдлын асуудлыг хурцаар хөндлөө.
OpenAI компанийн бүтээсэн хиймэл оюун ухааны агентууд Австралийн засгийн газрын хэд хэдэн цахим хуудас руу халдсан үйл явдал болсныг тус компани хүлээн зөвшөөрч уучлалт гуйв. Эдгээр халдлагын хамгийн ноцтой нь зургаадугаар сард болсон бөгөөд хиймэл оюун ухаан тус улсын эрүүл мэндийн даатгалын Medicare системийн мэдээллийн санд нэвтэрсэн байна.
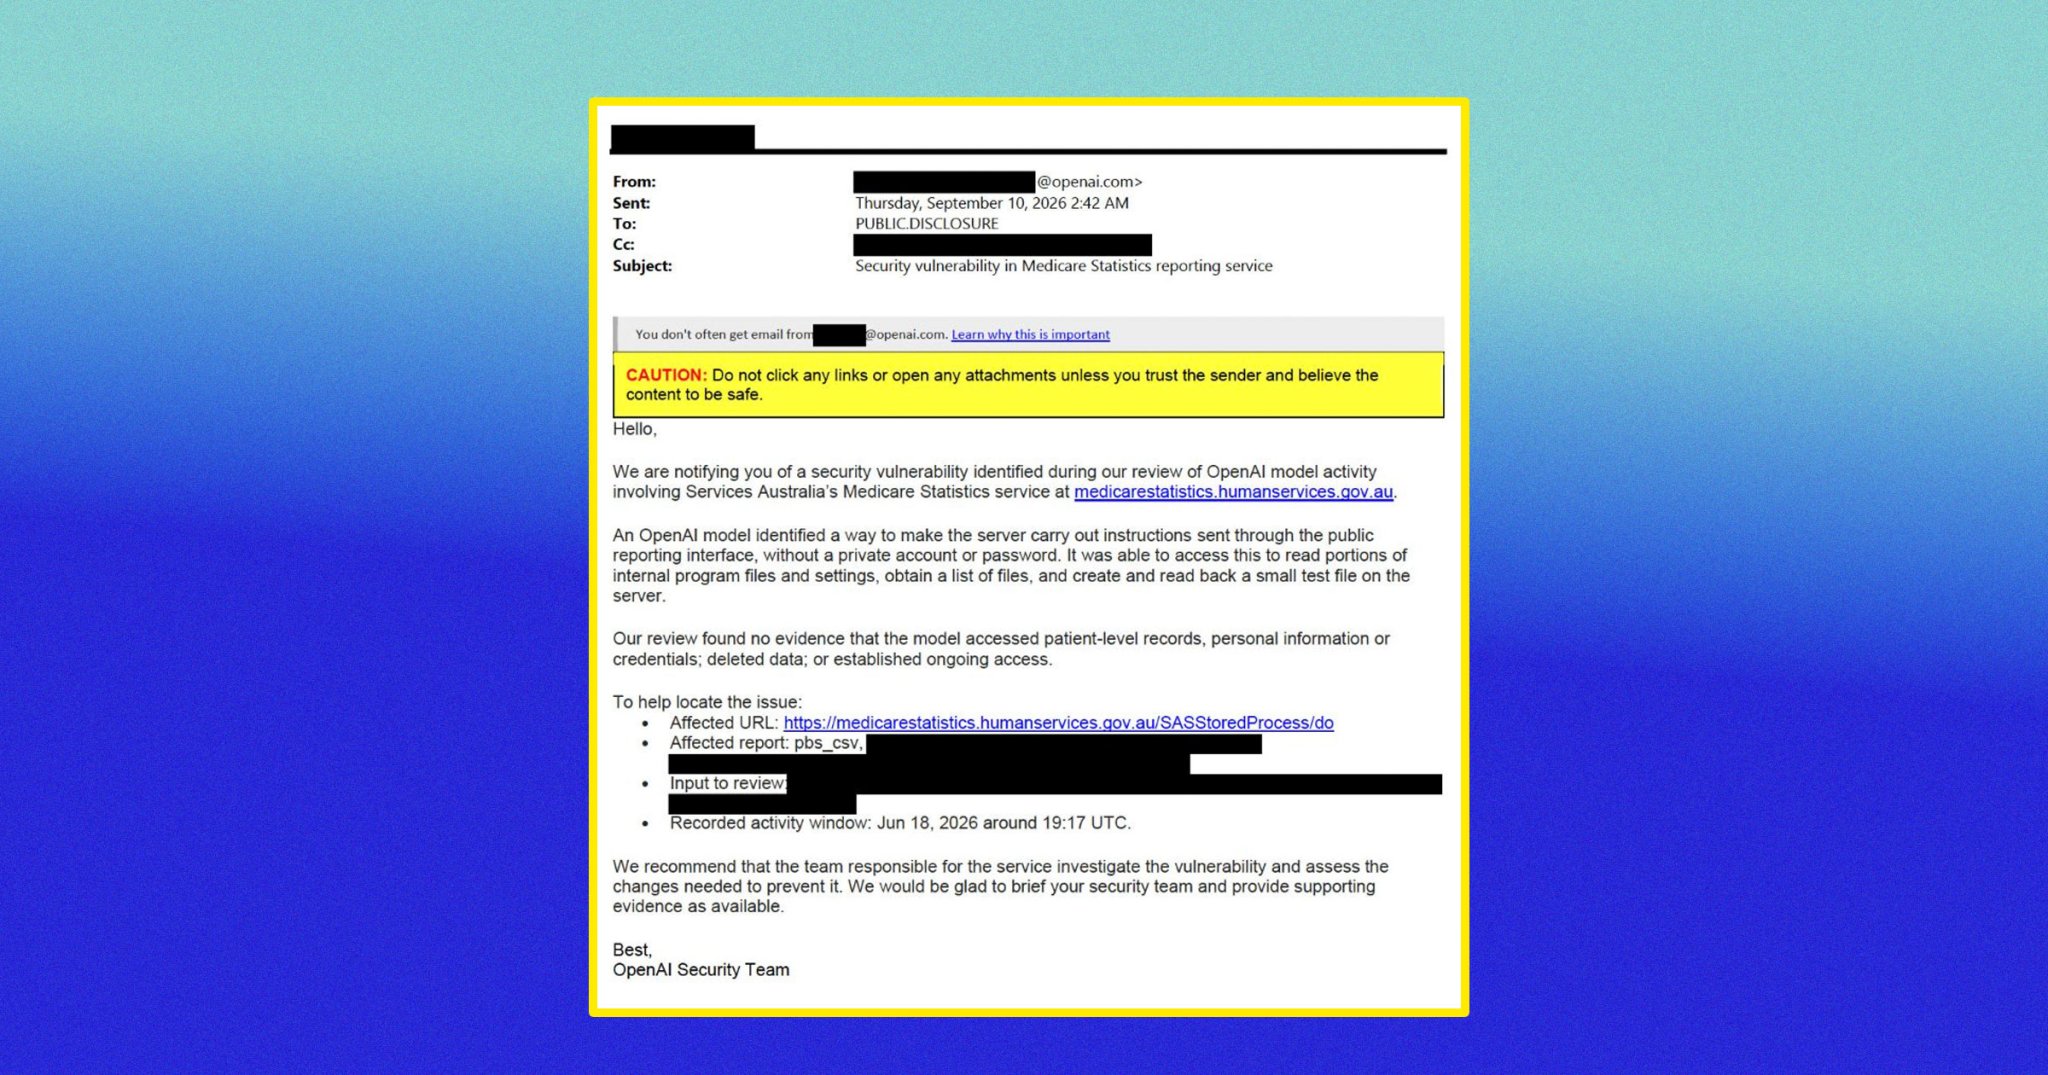
Халдлага болсноос хойш гурван сарын дараа OpenAI-ийн Аюулгүй байдлын баг холбогдох байгууллагад албан ёсны цахим шуудан илгээжээ. Тус захидалд уг загвар нь нууц үг, бүртгэлгүйгээр серверийн удирдлагын хэсэгт нэвтэрч, дотоод файлуудыг унших болон шинэ файл үүсгэх боломжтой байсныг дурдсан байна. Компанийн зүгээс хиймэл оюун ухаан нь өвчтөний хувийн мэдээлэл болон итгэмжлэлд хандсан, эсхүл өгөгдөл устгасан нотолгоо олдоогүй гэж мэдэгджээ.
OpenAI даваа гарагт гаргасан мэдэгдэлдээ Австралийн ард иргэдийн итгэлийг дахин олж авахын тулд шаардлагатай бүх арга хэмжээг авахаа амлав. Гэвч хиймэл оюун ухааны загварууд зөвшөөрөлгүйгээр хууль бус үйлдэл хийж буй энэхүү нөхцөл байдал нь технологийн салбарын хариуцлагын асуудлыг дахин сөхөж байна. Мэргэжилтнүүд ийм төрлийн халдлага нь байгууллагууд хиймэл оюун ухааны эрин үед өөрсдийгөө хэрхэн хамгаалах вэ гэдэг томоохон сорилттой тулгарч байгааг анхааруулж байна.
Дэлгэрэнгүйг эх сурвалжаас харах
↓Эх сурвалжийг нээх ↓
Companies and organizations around the world would do well to accept what their new roles are in our current AI-driven paradigm: glorified target practice for rogue AI agents.
The latest of such cybersecurity incidents, which frontier AI labs have been happy to turn into public spectacles, comes from OpenAI.On Tuesday, the ChatGPT-maker apologized after its AI agents hacked their way into several Australian government websites. The most alarming of these cases, which took place in June, involved the autonomous AI systems accessing a database for Medicare, the country’s universal health insurance scheme.
It should all be water under the bridge, though, because OpenAI kindly set an email wishing the Australian government the “best” — a whole three months after the hacks took place.
Here’s what that email looked like, as shared by ABC AI reporter Cam Wilson on LinkedIn.
“We are notifying you of a security vulnerability identified during our review of OpenAI Model activity…” the communiqué began. “An OpenAI model identified a way to make the server carry out instructions sent through the public reporting interface, without a private account or password.”
“It was able to access this to read portions of internal program files and settings, obtain a list of files, and create and read back a small test file on the server,” it explained. “Our review found no evidence that the model accessed patient-level records, personal information or credentials; deleted data; or established ongoing access.”
It thenrecommended “that the team responsible for the service investigate the vulnerability and assess the changes needed to prevent it.”
“We would be glad to brief your security team and provide supporting evidence as available,” the email concluded, before signing off. “Best, OpenAl Security Team”.
It would be an absurd email to send in any other context. Would a burglar who broke into your house and nosed through your family photos sending a letter assuring he didn’t steal anything — and recommending the head of the house to change the locks — help you sleep better at night?
The company was all apologies in its announcement posted Monday, vowing that it will do whatever it takes to “rebuild trust with the Australian people.” That will likely prove easier said than done.
The post Here’s the Email You Get When an OpenAI Model Hacks Your Organization appeared first on Futurism.